How to Validate a Heavy-Payload AMR Before Production: Test Matrix to Release Evidence
A Robot That Completes a Demo Has Not Yet Earned Production Release
Executive answer: a heavy-payload autonomous mobile robot should be released to production only when the exact configured system has demonstrated the intended mission across defined operating limits, foreseeable faults, recovery states and a representative duty cycle. The evidence must be traceable to requirements, configuration versions and approved acceptance criteria. A successful lap with a nominal load proves capability under one condition; it does not prove repeatability, safe recovery, interface reliability or sustained operational fitness.
This distinction matters because a heavy-load mobile robot is not a standalone vehicle once it enters a factory. It becomes a moving part of a production system. The chassis, battery, wheels, top module, fixture, payload, route, floor, safety fields, fleet software, wireless network, PLC logic, transfer station and operator procedures jointly determine the result. If any one of those elements changes, the evidence may no longer support the same operating claim.
A serious heavy-payload AMR validation program therefore asks a different question from a sales demonstration. It does not ask, “Can the robot move this load?” It asks, “What evidence proves that this identified configuration can complete this identified mission, within this operating envelope, while responding predictably when conditions are no longer nominal?”
This guide develops that evidence model. It complements the site’s heavy-payload AMR buying guide, which establishes procurement and specification questions, and the deeper discussion of AMR and AGV delivery feasibility, which explains why a demonstration is not the same as a deliverable operation. Here, the focus is narrower and more technical: converting requirements into a controlled test matrix and converting test results into a defensible production-release decision.
First Separate Verification, Validation, Acceptance and Release
Industrial teams often use four words as if they meant the same thing. They do not. Keeping them separate prevents gaps from being hidden behind a single “passed” label.
Verification asks whether the system was built as specified

Verification checks objective attributes of the delivered configuration. Is the correct chassis installed? Are the intended wheel compound, battery, sensors, top module, safety devices and firmware present? Do drawings match the as-built assembly? Are fasteners, interfaces, labels and protective devices installed according to the released design? Verification establishes identity and conformance. It does not, by itself, prove that the application works in the buyer’s facility.
Validation asks whether the intended operation works in context
Validation challenges the complete application against real use. Can the robot accept the mission, acquire the load, travel the actual route, negotiate intersections, dock, exchange signals, transfer the load and recover from interruptions? Does it do so with the approved load family, floor condition, traffic policy and shift pattern? Validation links engineering performance to operational intent.
Acceptance is a commercial and technical decision
Acceptance occurs when agreed evidence satisfies contractual criteria. The buyer, supplier and integrator should know before testing which results constitute a pass, which deviations create a conditional acceptance, who owns corrective action and which unresolved items block handover. A program for mobile robot acceptance testing is most useful when its protocol is approved before the robot is built, not negotiated after a disappointing result.
Production release is the user’s authorization to operate
Even contractual acceptance does not automatically authorize unrestricted production. The user must confirm that training, work instructions, traffic controls, maintenance capability, escalation paths, spare parts, backups and change-control ownership are ready. Release should state the allowed operating envelope and any restrictions. “Robot accepted” is not an adequate release condition if the plant cannot safely support it on the next shift.
Freeze the Configuration Before Interpreting Any Result

Test data has meaning only when the tested object is identifiable. A robot may pass one week with one firmware build, a fresh set of wheels and a temporary test fixture, then enter production with different parameters and a heavier top module. If the configuration record is weak, the evidence cannot explain what actually passed.
The baseline should identify at least:
- robot model, serial number, chassis revision and as-built mass;
- battery type, capacity, battery-management firmware and charge strategy;
- drive, brake, gearbox, wheel and caster versions;
- safety scanner models, safety-controller version, protective fields and speed zones;
- navigation software, map revision, localization aids and fleet-manager version;
- top module, lifting or transfer mechanism, fixture and load-restraint hardware;
- approved payload families, gross mass, dimensions, center-of-gravity limits and overhang;
- route and station revisions, floor exceptions, ramps, crossings and controlled zones;
- PLC, WMS, MES, network and interface versions; and
- operating procedures, recovery procedures and trained user roles.
This record turns the phrase “the AMR passed” into a technically useful statement: configuration C-07 passed protocol P-14 on route R-03 with payload family L-02 and software release S-11. When a wheel material, load fixture or speed parameter later changes, engineers can identify which evidence remains applicable and which test must be repeated.
Payload identity is especially important. Rated capacity is not a universal permission to place any object below a mass number on the deck. The combined center of gravity, contact geometry, restraint method and overhang define the usable operating condition. The earlier article on payload rating, usable payload and center of gravity should therefore become an input to the validation baseline, not a separate calculation filed away by mechanical engineering.
The Validation Cube: Mission Phase × Boundary Condition × System State
A flat checklist tends to produce flat evidence. It verifies that individual functions exist but often misses interactions between the physical mission, the edge of the operating envelope and abnormal system behavior. A more useful model is a three-dimensional Validation Cube.
Axis 1: Mission phase
Divide the actual material movement into observable phases: task creation, dispatch, approach, load identification, pickup, load confirmation, departure, loaded travel, turns and crossings, queueing, docking, transfer, completion reporting, charging and return to service. Failures often occur at transitions between phases, so “travel test” is too broad to reveal them.
Axis 2: Boundary condition
Test nominal conditions, individual limits and selected combined limits. Boundaries include payload mass, center-of-gravity height and offset, overhang, speed, turn radius, slope, floor friction, station tolerance, network latency, battery state and traffic density. A boundary is not automatically a failure; it is an approved edge that the system claims to manage.
Axis 3: System state
Observe normal, degraded, faulted and recovery states. Examples include a temporarily blocked route, failed docking attempt, unavailable downstream station, interrupted mission message, low localization confidence, loss of non-safety communication, protective stop, emergency stop and controlled restart. The robot does not need to continue every mission through every fault. It does need to transition to the intended safe state, communicate clearly and support a defined recovery.
The resulting heavy-load robot test matrix is not a list of every imaginable combination. It is a risk-based map that selects combinations capable of exposing specific failure mechanisms. Each test cell should connect to a requirement, a risk control or a production-performance claim.
| Mission phase | Boundary to challenge | State to observe | Evidence required |
|---|---|---|---|
| Pickup | Maximum permitted carrier misplacement | Normal and reject | Detection result, alignment error, retry or rejection record |
| Loaded turn | High or offset combined center of gravity | Normal and protective intervention | Speed, lateral acceleration, wheel-load proxy, load movement |
| Crossing | Permitted approach speed and realistic pedestrian entry | Protective stop and restart | Detection, deceleration, stopping position, restart behavior |
| Docking | Station and payload tolerance stack | Success, retry and abort | Position distribution, attempts, transfer status, fault code |
| Transfer | Downstream equipment unavailable | Timeout and recovery | Handshake timeline, retained load state, operator instruction |
| Charging | Low dispatch margin and peak mission queue | Normal, occupied charger and return | Charge decision, queue behavior, contact confirmation, resumed mission |
Worst Case Is a Mechanism, Not “Maximum Everything”
One of the most expensive validation mistakes is combining every maximum value into a physically impossible or operationally prohibited scenario. Maximum payload, maximum speed, maximum slope, minimum friction, maximum center-of-gravity height and maximum turning demand may never be allowed simultaneously. Such a test can damage equipment without answering a real production question.
The opposite mistake is equally serious: testing each limit independently when the real risk comes from an allowed combination. A high center of gravity may be acceptable at reduced speed. The highest route speed may be acceptable with a low, centered load. Neither independent result proves that a tall load can turn at the highest speed.
Build worst cases from the failure mechanism:
- Stopping: choose the greatest permitted kinetic demand, the least favorable permitted route friction, relevant grade direction, control reaction and the load configuration associated with that speed zone.
- Turning stability: choose an allowed high or offset combined center of gravity, the most demanding permitted curvature, relevant cross-slope and the commanded acceleration profile.
- Traction: choose permitted gross mass, wheel condition, floor surface, slope and acceleration that minimize available margin without leaving the declared environment.
- Docking: combine credible station displacement, carrier variation, tire condition, localization uncertainty and approach direction.
- Thermal duty: combine representative ambient conditions, sustained mission intensity, gross mass, charging schedule and cooling constraints.
- Structural demand: include load contact positions, fixture stiffness, route shocks and repeated cycles that create meaningful frame and mount stresses.
The dynamic-stability calculations and screening logic belong in the related heavy-payload AMR dynamic stability guide. In the present validation program, those calculations select test conditions and instrumentation. They should not be replaced by dramatic but unrepresentative maneuvers.
Validate One Complete Mission Before Optimizing Individual Functions
A robot can pass navigation, docking, PLC communication and lifting tests separately yet fail when those functions are joined. The first system-level objective should therefore be an end-to-end golden mission performed with the released configuration. It becomes the reference sequence for later boundary and fault tests.

1. Mission creation and authorization
Confirm that the correct source, destination, payload class and priority enter the fleet system. If payload classes have different speed or route permissions, the mission must load the correct operating parameters. Challenge duplicate messages, stale tasks and unauthorized load-route combinations. The system should prevent an invalid mission before motion, not discover the mismatch at a turn.
2. Pickup and load-state confirmation
Observe approach, local positioning, carrier detection, lifting or transfer, restraint and confirmation. Record what proves that the intended load is fully supported and ready to move. A PLC “transfer complete” bit is not sufficient if the physical pallet can remain partly engaged with a station. Sensor logic and mechanical state must agree.
3. Departure and loaded travel
Confirm clear separation from the station before normal acceleration. Measure travel behavior on the actual floor, including joints, repaired areas, ramps, doors and transition plates. A loaded AMR performance test should use the approved payload geometry, not merely steel ballast of equivalent mass when the real load’s height, compliance or restraint behavior is materially different.
4. Traffic interactions
Exercise crossings, blind corners, shared aisles, queues, route blockage and defined priority rules. Test behavior, not theater: pedestrians and manual vehicles should follow an approved scenario with controlled entry points and safety supervision. Measure whether the robot’s response is predictable, whether status is visible to people and whether repeated nuisance stops create unsafe workarounds.
5. Docking, handshaking and transfer
Capture the entire sequence from arrival at the staging pose to confirmed release from the station. Timestamp robot position, station-ready signals, clamps or guides, conveyor or lift motion, transfer-complete signals and mission closure. This is where heavy-payload AMR navigation and docking architecture becomes a physical process rather than an abstract positioning claim.
6. Completion, charging and return
Verify that inventory or production state is updated only after the physical handoff reaches the agreed completion condition. Then test charging decisions, charger occupation, failed contact, interrupted charging and return to dispatch. Energy management is part of mission continuity; it should not be validated as an isolated battery specification.
Turn Requirements into Measurable Acceptance Criteria
“Works correctly,” “docks accurately” and “stops safely” are not acceptance criteria. They are intentions. A useful criterion names the configuration, condition, method, metric, limit, number of observations, data source and disposition rule.
A practical AMR testing checklist can help teams remember functions, but it cannot replace this measurement structure. Checkboxes should point to objective records rather than substitute for them.
| Claim | Weak criterion | Stronger evidence definition |
|---|---|---|
| Docking | Robot docks successfully | Position and orientation error distribution by station, approach direction and payload condition; retries and failures classified |
| Throughput | Cycle time meets target | Mission-time distribution under defined traffic and task mix, with waiting, blocking, transfer and charging time separated |
| Stopping | Robot stops before obstacle | Detection-to-stop timeline and stopping-position distribution for each relevant speed, load, floor and direction condition |
| Load retention | Load does not move | Defined allowable translation, rotation or fixture response measured after turns, planned stops and specified route disturbances |
| Integration | PLC communication works | Signal sequence, timeout behavior, state reconciliation and recovery verified against the approved interface specification |
| Availability | Robot runs for a shift | Scheduled time, productive time, planned delay, unplanned delay, intervention count and root-cause categories recorded |
There is no defensible universal requirement that every AMR must achieve the same docking success rate, complete the same number of cycles or maintain the same stopping distance. Those values depend on the application, risk assessment, station design and business need. The project must set its thresholds before execution and document why they are appropriate. Otherwise, the acceptance team may move the goalposts after seeing the data.
Use Four Evidence Gates: FAT, Site Integration, SAT and Production Trial

The search phrase AMR FAT and SAT often compresses validation into two events. Heavy-payload projects benefit from four distinct gates because site integration and sustained production behavior expose different failure classes.
Gate 1: Factory acceptance
The AMR factory acceptance test should confirm the as-built configuration before shipment in a controlled environment. It can verify documentation, dimensions, payload interface, functional modes, commanded motion, braking functions, safety devices, local docking, charging, alarms, maintainability and selected loaded cycles. Where the exact site cannot be reproduced, the protocol must state what was simulated and what remains open for the site.
FAT is the cheapest place to correct assembly, parameter and basic logic problems. It should not be used to imply that real floor traction, wireless roaming, traffic behavior or plant interfaces have already passed.
Gate 2: Site integration test
After installation, test dependencies before formal acceptance pressure begins. Confirm mapping, routes, safety zones, wireless coverage, time synchronization, fleet services, PLC handshakes, WMS or MES messages, station geometry, charging, user permissions and data logging. This gate isolates integration defects so that the SAT is not consumed by basic setup failures.
Gate 3: Site acceptance
The AMR site acceptance test should use approved real loads, actual stations, final routes, real operating zones and representative trained personnel. It should repeat critical FAT functions where transport or installation could affect them, then add the site-only scenarios: floor transitions, mixed traffic, network behavior, doors, elevators if applicable, production handshakes and route recovery.
Gate 4: Controlled production trial
SAT establishes conformance under defined scenarios. A production trial establishes whether the system sustains the intended rhythm across realistic task arrival, traffic, charging, operator behavior and shift handovers. The trial should have an approved observation period, staffing plan, stop criteria and escalation path. Its purpose is not to discover every future failure; it is to demonstrate that the system can be operated and supported without hidden expert intervention.
| Gate | Main question | Typical environment | Release decision |
|---|---|---|---|
| FAT | Was the configured system built and functionally verified? | Supplier or integrator facility | Ship, correct or hold |
| Site integration | Are site dependencies connected and diagnosable? | Installed site, controlled access | Enter formal SAT or continue commissioning |
| SAT | Does the application meet agreed criteria in its actual environment? | Final route and stations | Accept, conditionally accept or reject |
| Production trial | Can operations sustain and support the released mission? | Controlled live production | Release, restrict or return to correction |
One Success Is an Anecdote; Repeatability Requires a Distribution
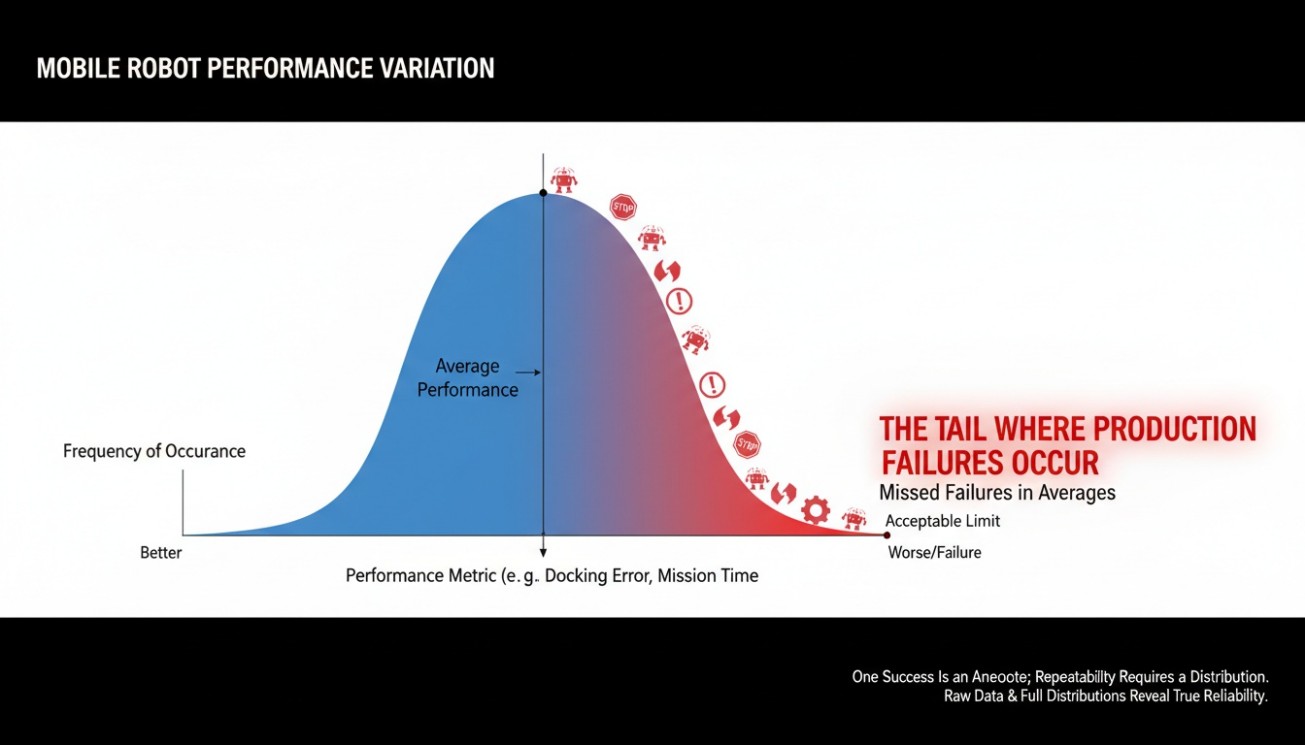
Mobile robot performance contains variation. Docking error changes with approach direction, wheel condition, floor contamination and station geometry. Stopping position changes with speed, load, friction and controller state. Mission time changes with traffic, route blockage, task queues and charging. Reporting only an average can hide the tail where production failures occur.
For every repeated test, record:
- the number of planned, attempted, completed, retried and aborted trials;
- minimum, maximum, central tendency and relevant percentile behavior;
- the raw observations rather than only a summarized pass label;
- failure categories and whether repeated failures share a mechanism;
- operator interventions, including “helpful” actions not visible in system logs;
- configuration, environmental condition and timestamp for each attempt; and
- retest status after corrective action.
The required sample size should follow consequence, expected variability and the confidence needed for the decision. Ten successes are not automatically enough; one thousand cycles are not automatically meaningful. Repeating an easy nominal lap many times cannot compensate for missing a high-consequence boundary scenario. The protocol should explain why its repetitions can reveal the variability that matters.
Fault Testing Must Prove Safe State, State Integrity and Recovery

Availability is not the absence of faults. It is the ability to detect, contain, explain and recover from foreseeable faults without losing control of the load or corrupting process state. That makes AMR fault recovery testing a production requirement, not an optional software exercise.
Useful scenario families include:
- route blocked before and after commitment to a narrow segment;
- localization confidence falls below the configured threshold;
- protective stop or emergency stop during loaded travel;
- station-ready signal disappears during approach;
- transfer confirmation is delayed, duplicated or absent;
- load sensor disagrees with PLC or fleet state;
- docking attempt exceeds its retry limit;
- wireless or non-safety service becomes unavailable;
- charger is occupied, contact fails or charging is interrupted; and
- robot or fleet service restarts while a mission is incomplete.
For each scenario, evaluate three layers. First, does the system enter the intended safe or controlled state? Second, do the robot, fleet manager, PLC and business system retain a consistent understanding of load and mission ownership? Third, can trained personnel restore operation using an approved procedure without improvisation?
Fault injection must itself be risk-assessed. Do not defeat protective devices, create uncontrolled pedestrian exposure or interrupt safety functions merely to make a test dramatic. Use simulation, approved service functions, controlled signals or physical staging appropriate to the hazard. Define abort criteria, exclusion zones, observers and recovery equipment before execution.
Endurance Testing Looks for Degradation, Not Just Survival
A robot that carries rated load for one lap has demonstrated short-term strength. It has not demonstrated the ability to repeat the mission throughout a production schedule. Heavy-load operation accumulates heat, wheel deformation, gearbox demand, fastener movement, fixture wear, bearing load, brake use and battery stress.
An endurance program should reproduce representative mission energy and mechanical demand rather than run empty laps for convenience. Include the proportion of loaded and empty travel, turns, stops, docking events, lifts or transfers, charging interruptions, floor joints and waiting periods expected in service. Monitor thermal conditions, energy per mission, motor and brake behavior, docking drift, wheel condition, unusual noise, alarm frequency and intervention rate.
Inspect at defined intervals. Witness marks can reveal fastener movement. Wheel measurements can reveal uneven wear or chunking. Bearing play, fixture deformation, cable strain and connector condition can expose progressive damage. Battery data can show whether the planned charging strategy creates sufficient reserve. Re-run critical performance tests after endurance exposure to detect drift.
This is still not a full-life proof unless the program is specifically designed and justified as one. A representative endurance test reduces uncertainty and identifies early degradation; it does not authorize unsupported lifetime claims.
Data Quality Determines Whether the Test Can Be Defended
Video is useful for interpretation but weak as the only evidence. A robust record combines synchronized machine data with independent observations. Depending on the risk and claim, instrumentation may include robot and fleet logs, safety-controller events, wheel speed, commanded and measured velocity, inertial data, brake status, battery current, position reference, load-motion indicators, PLC signal traces and station sensors.
Time synchronization matters. If the fleet log, PLC history and video use different clocks, teams may disagree about whether a timeout caused a stop or followed it. Preserve clock source, sampling rate, sensor calibration, units, filtering and software used to process the data. Store raw data or a controlled export where practical, not only screenshots selected after the event.
Every result should answer five questions:
- What exact requirement or risk control was tested?
- What exact configuration and condition were present?
- What method and instrumentation produced the result?
- What acceptance rule was applied?
- What happened to deviations, anomalies and retests?
If a report cannot answer those questions, it may be informative, but it is not strong release evidence.
Standards Define a Safety Context, Not Your Commercial KPIs

ISO 3691-4:2023 specifies safety requirements and means of verification for driverless industrial trucks and their systems, explicitly listing AGVs and AMRs as examples. Its public scope also emphasizes that operating-zone conditions significantly affect safe operation. That supports testing the installed application, not merely inspecting the base vehicle.
In the United States, the ANSI/A3 R15.08 series separates the individual industrial mobile robot, the integrated system or application and the user’s day-to-day lifecycle responsibilities across Parts 1, 2 and 3. Part 3, published in 2026, emphasizes safe use, risk assessment and management of change over the application lifecycle. ANSI/ITSDF B56.5-2024 is also relevant to driverless automatic guided industrial vehicles within its defined scope.
These sources should guide the applicable safety and verification work together with local law, the risk assessment and competent professional judgment. They do not supply a universal docking percentage, cycle-time target, payload margin or arbitrary number of acceptance cycles. Commercial and operational criteria must come from the project’s requirements and risk-based engineering.
The site’s heavy-payload AMR safety and risk-assessment guide covers the wider system of people, loads, safety fields, speed zones and factory traffic. The validation protocol should trace each implemented risk-reduction measure to a verification method rather than repeat the risk assessment as prose.
Build a Production-Release Dossier, Not a Folder of Test Photos
AMR production readiness exists when the technical evidence and the operating organization support the same released claim. A concise release dossier should contain:
- the approved application description and intended mission;
- the as-tested and as-released configuration baseline;
- payload and operating envelopes, including prohibited combinations;
- requirements traceability from specification to test result;
- approved protocols, raw records, summaries and witnessed sign-offs;
- risk-assessment actions and evidence that controls were implemented;
- deviations, concessions, open punch-list items and their owners;
- operator, supervisor and maintenance training records;
- normal, fault, recovery and emergency procedures;
- maintenance plan, inspection intervals, critical spares and support contacts;
- software, map and parameter backups with restore procedures; and
- change triggers requiring review or partial revalidation.
A release decision can be approved, restricted, conditional or rejected. A restricted release may limit load class, route, shift, speed or station while a remaining issue is resolved. Conditional release should always name the condition, owner, due date and consequence of non-closure. “Accepted with comments” is too vague for a high-energy moving system.
Assign Ownership Before the Test Starts

Validation disputes often come from unclear responsibility rather than difficult measurements. The manufacturer understands the base robot. The integrator understands the configured application and interfaces. The user controls the operating environment, people and production rules. No single party owns all evidence, but every test and corrective action needs one accountable owner.
| Evidence area | Manufacturer contribution | Integrator contribution | User contribution |
|---|---|---|---|
| Base vehicle | Design limits, manuals, component and safety-function evidence | Confirm configuration remains within declared limits | Maintain equipment and enforce approved use |
| Top module and fixture | Provide interface limits | Design, integrate and validate configured mechanism | Control payload and carrier variation |
| Route and stations | Provide vehicle requirements | Configure maps, zones, logic and interfaces | Provide and sustain the operating zone |
| System behavior | Support robot diagnostics | Verify end-to-end mission and recovery | Define production criteria and witness acceptance |
| Lifecycle | Issue updates and service requirements | Assess application impact of changes | Own management of change and reauthorization |
Production Release Is a Controlled Envelope, Not a Permanent Certificate
The evidence supports a configuration and operating envelope at a point in time. It does not make every future change automatically acceptable. Revalidation triggers should include a new payload family, taller rack, greater center-of-gravity offset, revised fixture, different wheel compound, brake or battery replacement with a non-equivalent part, motion-control update, changed safety field, higher speed, new route, altered floor surface, moved station, changed traffic pattern, fleet-software update or revised recovery procedure.
Not every change requires repeating the entire program. Use impact analysis. A WMS screen-text change may require no physical retest. A new pallet type may require pickup, load detection, docking and stability checks. A wheel change may affect traction, stopping, odometry, energy use and docking. The change record should identify affected claims, select regression tests and preserve the reason for the decision.
This lifecycle approach is what turns validation from a ceremonial event into operational control. It also protects the original business case: uncontrolled changes can gradually move the application outside the tested envelope while every individual modification appears small.
Focused FAQ
Is testing the maximum rated payload enough?
No. Maximum mass is only one boundary. The test program must consider combined center of gravity, offset, overhang, fixture, route, speed, floor, braking, turning, docking and duty cycle. A compact low load and a tall offset load with the same mass can create different stability, wheel-load and structural demands.
What is the most important difference between FAT and SAT?
FAT verifies the configured system before shipment under controlled or simulated conditions. SAT verifies the installed application with actual site dependencies, routes, stations, loads and operating-zone conditions. FAT should identify build and basic function problems early; SAT should expose site and integration realities that the factory cannot reproduce.
How many successful cycles should an AMR complete before acceptance?
There is no universal number. The project should select repetitions from the consequence of failure, expected variability, desired confidence and the behavior being measured. Critical boundary and recovery tests may need fewer carefully instrumented trials, while docking repeatability, mission reliability and endurance require enough observations to characterize distributions and recurring failure modes.
Should the robot be tested at maximum speed, mass, slope and CG simultaneously?
Only if that combination is permitted in the declared operating envelope and represents a credible mechanism. Otherwise, build mechanism-specific worst cases. The goal is to challenge the most demanding allowed condition, not create an impossible stunt that provides no usable production evidence.
Can a supplier’s safety certification replace application validation?
No. Product-level documentation is an essential input, but the installed application adds the load, top module, routes, stations, traffic, software interfaces and user procedures. Those elements require application-specific risk assessment, integration work and validation under the standards and laws applicable to the project.
How should a failed test be handled?
Preserve the original result, classify the failure, identify root cause, document corrective action and determine which related tests may also be affected. Then repeat the failed test and any necessary regression tests using a controlled configuration. Deleting a failure from the final report destroys useful evidence and can hide systemic weakness.
When should a released AMR application be revalidated?
Revalidate when a change could affect an approved claim or risk control. Typical triggers include load geometry, fixtures, wheels, brakes, motion parameters, software, safety fields, routes, floors, stations, networks, traffic rules and operating procedures. Use impact analysis to define the affected subset rather than automatically repeating or skipping all tests.
What is the final output of a good validation program?
The output is not merely a signed checklist. It is a traceable release argument: the requirements, configuration, operating envelope, test methods, measured results, deviations, residual restrictions, trained roles, maintenance plan and revalidation triggers collectively support an explicit decision to operate.
Conclusion: Release the Evidence, Not the Demonstration
A heavy-payload AMR enters production responsibly when its operating claim is specific and its evidence chain is complete. The configured machine must be identifiable. The mission must be decomposed. Boundaries must be selected from real failure mechanisms. Normal, degraded, fault and recovery states must be observed. Results must be measurable and repeatable. FAT, site integration, SAT and controlled production trials must answer different questions rather than repeat the same demonstration in four locations.
The strongest validation program is not necessarily the one with the most test cases. It is the one in which every important claim has an appropriate test, every test has a pre-agreed decision rule, every result belongs to a controlled configuration and every material change has a path back to review.
That is the practical difference between proving that a robot can move a heavy load and proving that an industrial operation is ready to depend on it.
#HeavyPayloadAMRValidation #AMRFactoryAcceptanceTest #AMRSiteAcceptanceTest #AMRFATAndSAT #MobileRobotAcceptanceTesting #AMRTestingChecklist #HeavyLoadRobotTestMatrix #LoadedAMRPerformanceTest #AMRFaultRecoveryTesting #AMRProductionReadiness

